Starting with iOS 27.3, will Apple check the photos and files we keep on iCloud?
To find out, I read Apple’s support page on iCloud public links, published on November 3, 2026, and three articles from November 4, 2026, in six steps: from what Apple writes to what no source explains yet.
What does Apple write?
According to Apple’s support page, starting with version 27.3 of its operating systems (iOS, iPadOS, macOS and visionOS, that is, the ones for iPhone, iPad, Mac and Vision Pro), iCloud items shared with a public link will be “checked by Apple for harmful content.” That is the option called “Anyone with the link.” The page does not mention the rest of iCloud.
The page opens by saying that an item shared with that option “is made accessible to Apple to check for harmful content.” The examples are a photo in iCloud Photos and a file in iCloud Drive.
What is the difference between “People you choose” and a public link?
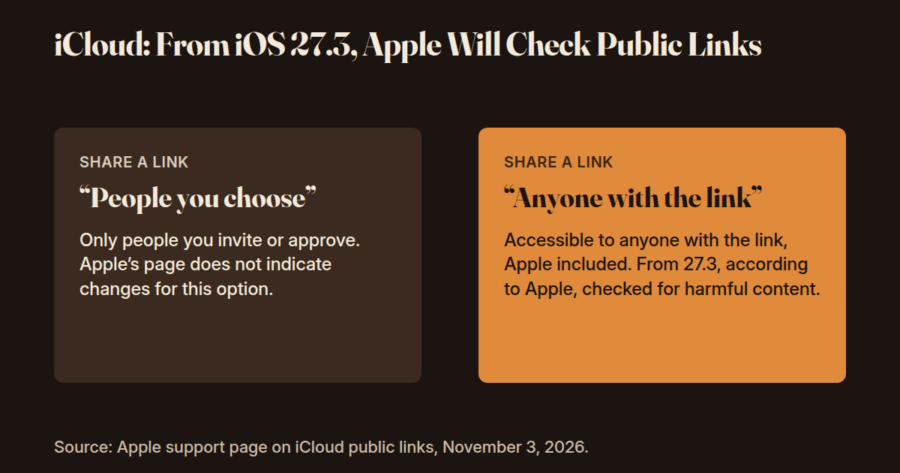
According to the page, when you share an iCloud item you can choose “Share a Link” or “Send a Copy.” With a link, there are two options:
- “People you choose”: only the people you invite or approve.
- “Anyone with the link”: the item is accessible to anyone who has the link, Apple included.
The new rule, according to Apple, concerns the second option; for the first, the page indicates no changes.
What does “no longer end-to-end encrypted” mean?
End-to-end encryption, according to Apple, is the protection under which data can be read only on your own trusted devices, where you are signed in with your Apple Account: no one else, not even Apple, can access it. Advanced Data Protection is an optional setting that extends this protection to more iCloud data, including photos, notes and backups.
For an item shared with a public link, the November 3 page says it is no longer end-to-end encrypted, even with Advanced Data Protection turned on.
But it is not new that this option makes the item accessible to anyone who has the link, Apple included: 9to5Mac writes so. What changes is that Apple says it will begin checking those links.
An Apple page from January 5, 2026 also lists content shared with a public link among the content without Advanced Data Protection.
What happens if Apple considers content harmful?
According to the page, anyone who tries to upload harmful content exposes the item to action: Apple reserves the right to move, refuse, modify, remove or delete it at any time. Apple may also act on the Apple Account: block or disable it; prevent the creation of a new account with the same email address or phone number; “if necessary,” involve law enforcement.
What do the news outlets say?
- What “harmful content” means. Apple does not define it. MacRumors writes that it could be malware (harmful software), malicious files or child sexual abuse material (CSAM), given that Apple mentions law enforcement. The Register suggests that it may also include other “potentially unlawful” content. These are the outlets’ hypotheses: Apple’s page names neither malware nor child sexual abuse material.
- How the check works. The Register writes that Apple has not explained how the checks will work and did not answer its questions. Apple writes “check” and “checked”; the verb “scanned” appears in The Register’s subhead, not on Apple’s page.
- Links already created. MacRumors writes that Apple does not say whether links created before the 27.3 updates will be checked.
- When it ships. 9to5Mac writes that the first beta of iOS 27.3 (a test version for developers, ahead of the public one) came out this week; according to The Register, on Tuesday. The Register and MacRumors give December for the public version, without citing a source. Apple’s page gives no dates and does not say whether the check already applies in the beta.
What do the sources not say yet?
- Italy and the European Union. The page only writes that not all features are available in all countries or regions.
- How the check works and where (on the device or on Apple’s servers): the page does not say; it writes that the item “is made accessible to Apple.”
- “Send a Copy.” The page does not name it among the items that are checked.
To the question that opens this article the sources answer like this: Apple writes that items shared with a public link will be checked. MacRumors and The Register read the rule the same way: it concerns only public links, not content shared directly with other people.
All that remains is to see, when the final version ships, whether Apple will explain how the checks work and for which countries.
Frequently asked questions
Will Apple check everything I have on iCloud?
According to Apple’s support page, the check concerns items shared with a public link (“Anyone with the link”). MacRumors and The Register read the rule the same way: it concerns only public links, not content shared directly with other people. Apple’s page does not mention the rest of iCloud.
What changes if I share with “People you choose”?
The new rule, according to Apple, applies to sharing with a public link. For “People you choose,” that is, only the people you invite or approve, the page indicates no changes. The page does not name “Send a Copy,” sending a copy, among the items that are checked.
What is end-to-end encryption?
According to Apple, it is the protection under which data can be read only on the owner’s trusted devices, not by Apple. For an item shared with a public link, Apple writes that it is no longer end-to-end encrypted, even with Advanced Data Protection turned on.
What is Advanced Data Protection?
According to Apple it is an optional setting that makes more iCloud data, including photos and backups, end-to-end encrypted. For a public link, according to Apple, the item is not end-to-end encrypted even if Advanced Data Protection is turned on.
Will the links I have already created be checked?
Apple’s page does not say. MacRumors notes that it does not clarify whether links created before the 27.3 updates will be checked. The Register also writes that Apple has not explained how the checks will work, or whether they will be carried out by people, automated systems or both.
Does it apply in Italy too?
Apple’s page names neither Italy nor the European Union. It only writes that not all features are available in all countries or regions. When the final version ships, we will see whether Apple explains for which countries it applies.
Method note (for those who want to check)
I read Apple’s pages and the three articles on November 5, 2026. The quotations in the text are in the original English; for the passages reported in paraphrase, these are the originals.
- Apple Support, page of November 3, 2026: “checked by Apple for harmful content”; “is made accessible to Apple to check for harmful content”; “Share a Link” / “Send a Copy”; “People you choose” (“only people you invite or approve”); “Anyone with the link” (“including Apple”); “the item is no longer end-to-end encrypted, even if the owner or participants have turned on Advanced Data Protection”; “If you try to upload harmful content, Apple reserves the right to move, refuse, modify, remove, or delete the content at any time”; “blocking the ability to create a new Apple Account with the associated email address or phone number”; “if necessary”; “Not all features are available in all countries or regions”.
- Apple Support, “iCloud data security overview,” January 5, 2026: “can be decrypted only on your trusted devices where you’re signed in to your Apple Account”; “No one else can access your end-to-end encrypted data — not even Apple”; “an optional setting that offers our highest level of cloud data security”; with Advanced Data Protection the number of end-to-end encrypted categories “rises to 25 and includes your iCloud Backup, Photos, Notes, and more”; content shared with “anyone with the link” does not support Advanced Data Protection.
- 9to5Mac: the option “has always made it accessible to anyone who has the link, including Apple”; “Apple says it will begin checking those public links for harmful content”; the first beta “this week”.
- MacRumors: “malware, malicious files, and/or child sexual abuse material (CSAM)”; “given Apple’s mention of law enforcement involvement”; “it’s only the latter option that will be evaluated by Apple”; “Apple does not say whether links created before the 27.3 updates will be checked”.
- The Register: “hasn’t explained how the checks will work”; “whether human moderators, automated systems, or both”; subhead: “Content shared with anyone who has the URL will be scanned for ‘harmful content’”; “potentially unlawful”; “applies only to iCloud content shared via links created to be accessible to anyone, as opposed to content shared directly with other people”; the beta “on Tuesday” (the calendar gives November 3, 2026); the public version “expected in December”.
The dates of the outlets are the ones printed on the pages: The Register November 4, 2026, 21:49 UTC; 9to5Mac November 4, 2026, 7:55 a.m. PT; MacRumors November 4, 2026, 11:12 a.m. PST. The release notes of the iOS 27.3 beta are not among the sources read.
Sources
Accessed on November 5, 2026. I mark the type of each source: primary (whoever writes the rule), secondary.
- Apple Support, “Learn more about sharing content that can be accessed by Anyone with the Link,” “Published Date: November 03, 2026.” Primary. https://support.apple.com/en-us/149168
- Apple Support, “iCloud data security overview,” “Published Date: January 05, 2026.” Primary. https://support.apple.com/en-us/102651
- Apple Support, “How to turn on Advanced Data Protection for iCloud,” “Published Date: April 17, 2026.” Primary. https://support.apple.com/en-us/108756
- The Register, Brandon Vigliarolo, “Apple turns iCloud into spy cloud, will start looking at public share links,” November 4, 2026. Secondary (draws on Apple’s page, with its own comments; the headline is the outlet’s judgment). https://www.theregister.com/security/2026/11/04/apple-turns-icloud-into-spy-cloud-will-start-looking-at-public-share-links/5307681
- 9to5Mac, Ryan Christoffel, “With iOS 27.3, Apple will start checking iCloud public links for ‘harmful content,’” November 4, 2026. Secondary. https://9to5mac.com/2026/11/04/with-ios-27-3-apple-will-start-checking-icloud-public-links-for-harmful-content/
- MacRumors, Juli Clover, “Apple Will Check Public iCloud Links for Harmful Content Starting in iOS 27.3,” November 4, 2026. Secondary. https://www.macrumors.com/2026/11/04/ios-27-3-icloud-link-check/